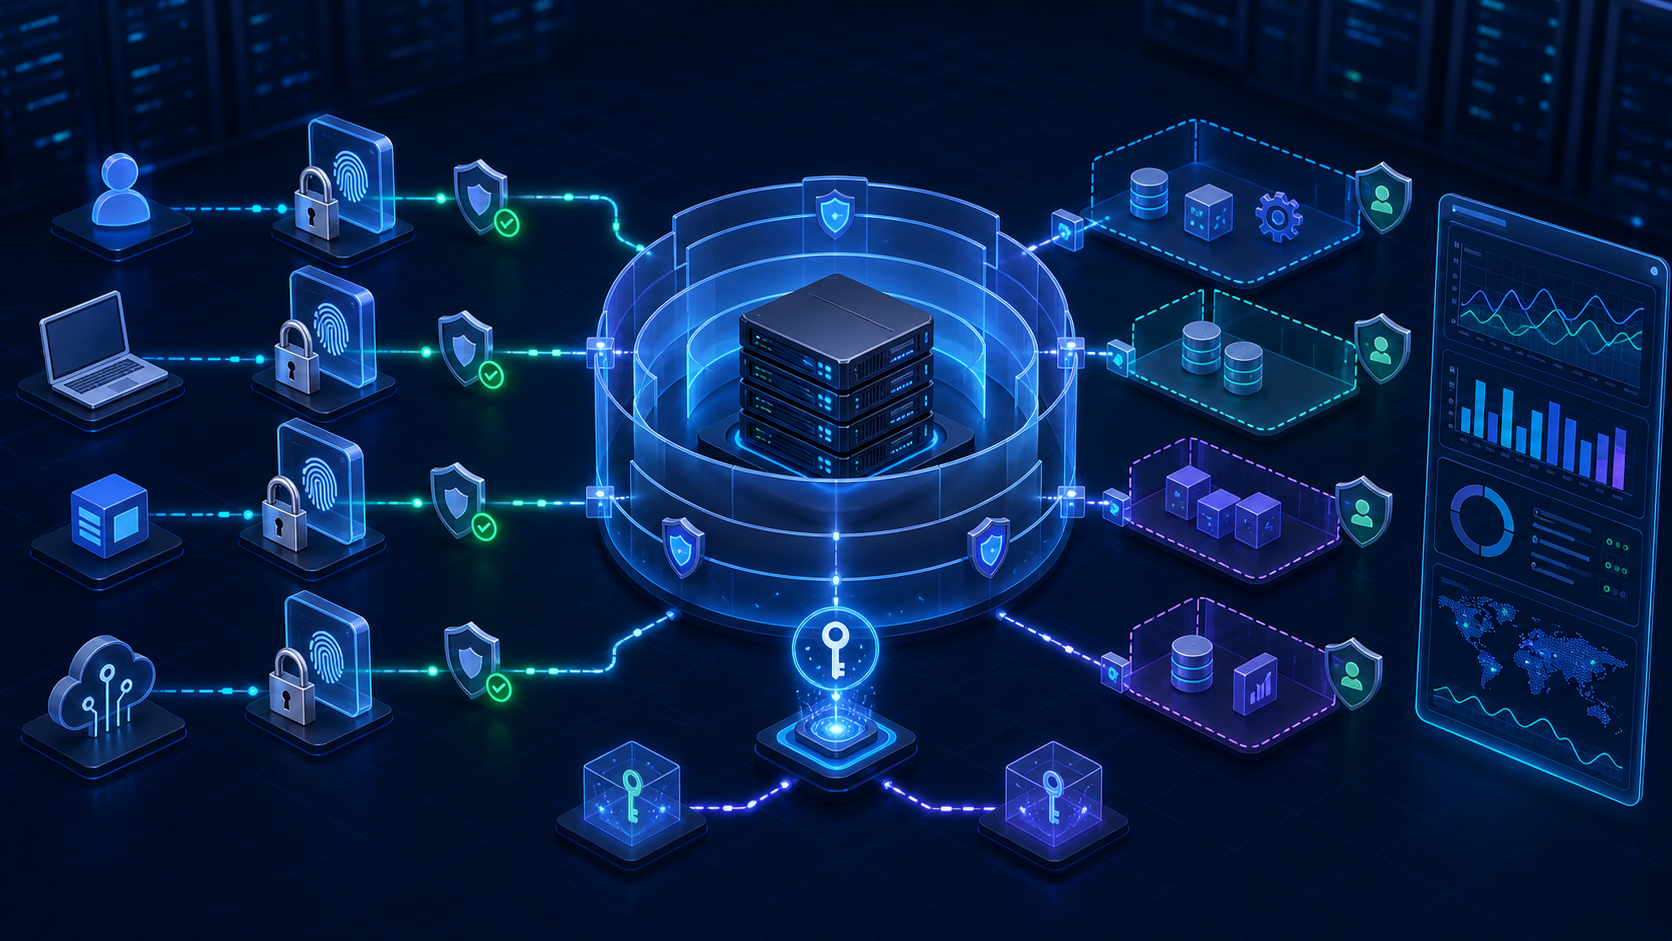
Zero-trust security treats every connection as untrusted until its identity and permissions have been verified.
Reduce the attack surface
Expose only required services, enforce key-based access, and apply least-privilege rules to administrators and applications.
Automate policy
Use repeatable firewall rules and continuous monitoring so server access stays aligned with your intended policy.