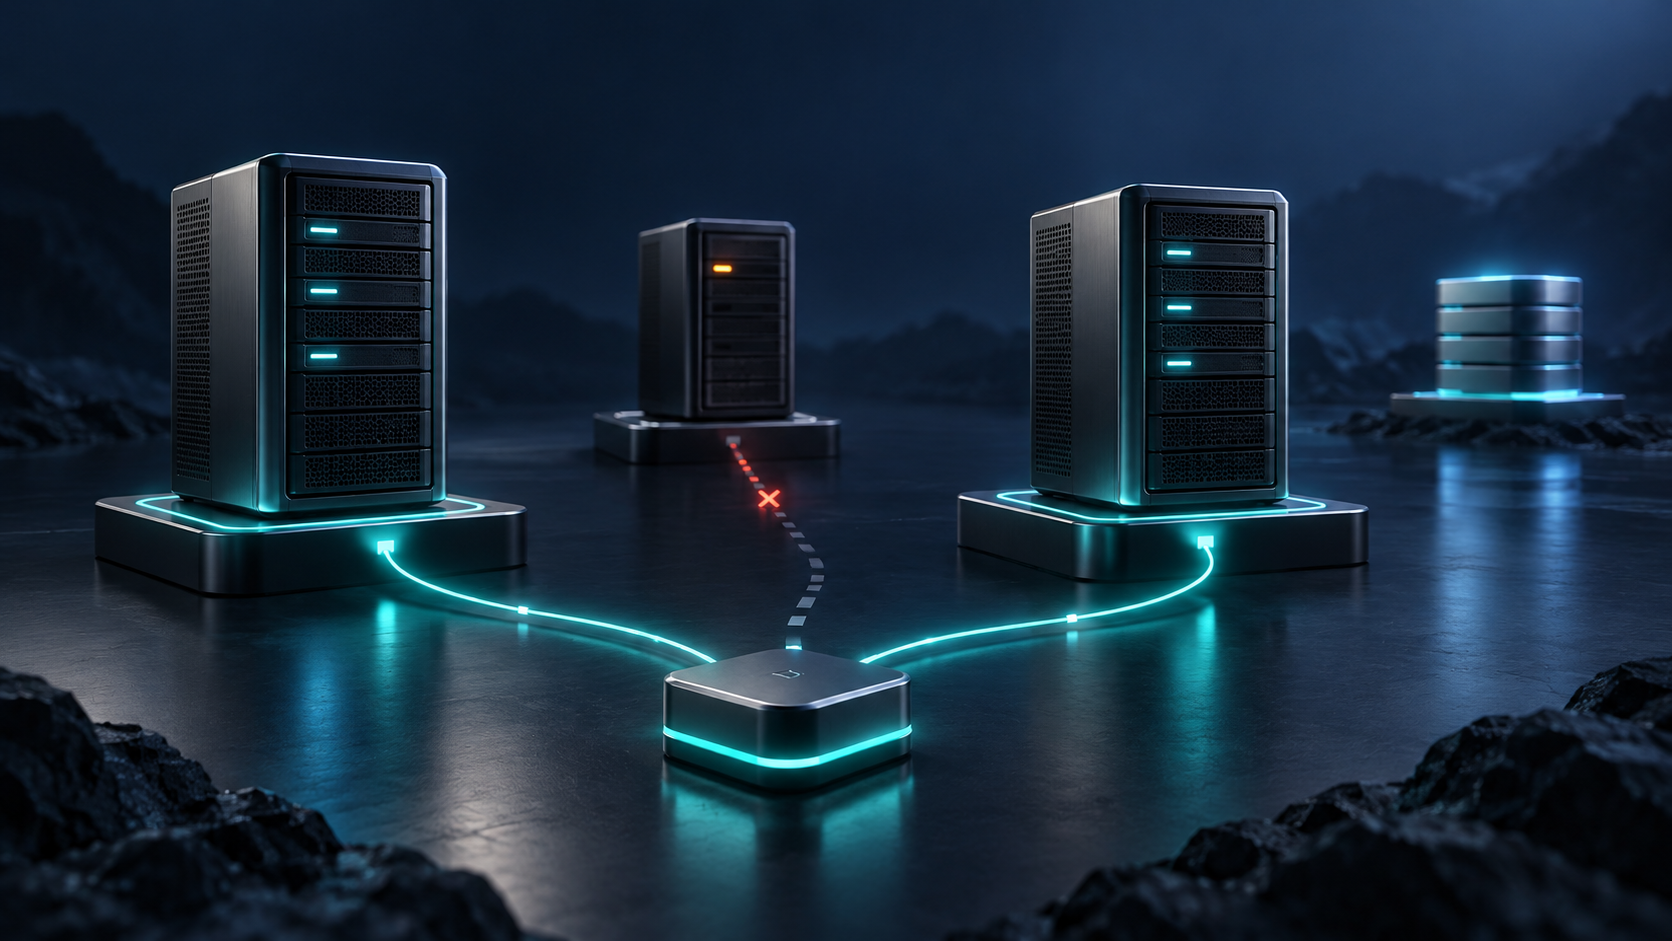
A reverse proxy receives requests on behalf of an application and forwards them to an upstream service. A load balancer distributes work across a set of available targets. In a VPS hosting setup, the same Nginx service can perform both jobs.
The useful distinction is between accepting and forwarding traffic, and deciding which application instance should handle it. Understanding those roles helps you choose a simple starting architecture and recognize what must change when one application process is no longer enough.
Reverse proxy vs load balancer at a glance
| Question | Reverse proxy role | Load balancing role |
|---|---|---|
| What does it do? | Accepts client requests for an application and forwards them upstream. | Selects a target from a configured group to distribute work. |
| Does it need several application instances? | No. One upstream application can be enough. | Several eligible instances provide the practical distribution benefit. |
| Typical VPS use | Expose a private Node.js or Python service through a public website endpoint. | Spread application requests across multiple processes or hosts. |
| Can one component do both? | Yes, when it forwards requests to a pool of application instances. | Yes, an HTTP load balancer can act as a reverse proxy. |
| Does it guarantee availability? | No. The proxy and its dependencies can still fail. | No. Healthy spare capacity and a resilient request path are also required. |
This article focuses on HTTP applications. Load balancing also exists for other traffic types; compare the actual protocol and routing capabilities of a product rather than relying on its name.
What a reverse proxy does for a VPS application
Suppose a Node.js process listens on a loopback address. Visitors use your public domain, and Nginx passes suitable requests to that process. The browser does not need to know the application's internal port.
HTTP's intermediary terminology describes a gateway, also called a reverse proxy, as the server-facing intermediary. Unlike a forward proxy chosen for a client's outgoing requests, it sits in the path to the hosted service.
You can route different hostnames or paths to different applications without balancing traffic between those applications. For example, sending the main website to one service and an API to another is routing. Sending API requests across three equivalent API instances adds load balancing.
Nginx's reverse proxy documentation covers forwarding requests, setting upstream headers, and buffering responses. For a practical single-application starting point, see our Node.js deployment guide for Ubuntu.
When load balancing becomes useful
Add application instances when measurements show that the application tier needs more capacity, or when you need to take an instance out of service while others continue handling requests. Check database capacity and other shared dependencies before assuming that more web processes will increase throughput.
One application instance:
Browser --> Nginx reverse proxy --> Application A

Several application instances:
Browser --> Nginx reverse proxy and load balancer
                      |--> Application A
                      |--> Application B
                      |--> Application C
These are conceptual layouts. A, B, and C might run on one VPS or on separate hosts. Multiple processes on one VPS still share its CPU, memory, storage, and failure risk.
For HTTP traffic, Nginx supports approaches such as round-robin distribution, least connections, and IP-based affinity. Its HTTP load balancing guide explains the choices. Select a method using request duration, instance capacity, and measured behavior; a different algorithm cannot repair an overloaded database.
Choose the layout around the failure you need to handle
For a small application, one VPS with a reverse proxy and a supervised application process may meet the operating requirements. Add another process when the workload and available resources justify it.
If surviving the loss of an application host is a requirement, place suitable application capacity on another host. Then examine the proxy, network path, database, and shared storage. A single proxy VPS can remain the point whose failure makes every healthy application instance unreachable.
A provider-managed load balancer is one option to evaluate. Services such as AWS Elastic Load Balancing offer target distribution and health monitoring, but you still need to assess placement, configuration, costs, and the application's dependencies for your own design.
Write a concrete requirement before adding components: “The site should keep serving essential requests while one application instance is stopped.” Test that requirement, then decide whether host-level resilience is also necessary.
Make health checks and retries match the application
Traffic distribution is useful only when the selected target can do the required work. A process that accepts a connection may still fail because it cannot reach its database or has loaded the wrong configuration.
Passive checks infer failures from real requests. Active checks send separate probes on a schedule. Nginx's health-check documentation describes both approaches; verify which features your selected edition and version provide.
For passive upstream handling, max_fails and fail_timeout control failure accounting and temporary unavailability. The upstream reference also documents exceptions, including the behavior of a group with only one server. Do not treat a one-target configuration as a failover system.
Use readiness checks that reflect the service's essential dependencies, with bounded execution time. Test what happens when all targets fail and when a recovered target returns.
Review retry behavior separately. Nginx's upstream retry rules distinguish non-idempotent requests. A lost response does not prove that a write never happened. Keep retries bounded and use application-level duplicate protection for actions such as order creation.
Prepare sessions, files, and background work for multiple instances
Load balancing exposes assumptions that were harmless when every request reached one process. Test a login on instance A followed by an authenticated request on instance B. Repeat that check for uploads and any temporary workflow state.
- Sessions: use a compatible shared session store or another deliberately designed session mechanism.
- Uploads: ensure every instance that serves a file can access it through the intended storage design.
- Configuration: keep required secrets, cookie settings, and data formats compatible across the active instances.
- Scheduled work: coordinate task execution so adding an application instance does not duplicate the schedule.
- Database connections: add up connection demand from every web and worker process, including deployment overlap.
The Twelve-Factor guidance on processes provides useful context for keeping persistent state outside individual application processes. Session affinity may help an application that requires it, but it does not make state stored on a failed instance available elsewhere.
Define HTTPS and client-IP handling at every hop
If HTTPS terminates at the reverse proxy, the connection from the proxy to the application is a separate connection. Decide how that hop is protected. For remote upstreams, configure encryption and certificate verification where required; Nginx documents TLS to upstream servers. An encrypted browser connection alone does not establish protection for every internal hop.
Applications may otherwise see the proxy's address as the client address. Forwarded headers can carry information about the original request, but they require a defined trust boundary.
MDN's X-Forwarded-For guidance explains the risk of using spoofable values for rate limiting or access decisions. Trust only the intended proxy chain, restrict direct access to application ports, and configure the application to accept forwarded information only from those trusted sources.
If Nginx itself sits behind another proxy, its real IP module provides explicit trusted-address settings. Test the complete path with your actual CDN or load balancer rather than copying a broad trust rule.
Test long-lived traffic and observe the complete request path
A successful homepage response does not validate uploads, downloads, streaming, or live connections. Exercise the traffic types your users depend on.
For WebSockets, Nginx requires explicit handling of the upgrade headers, and idle-timeout behavior must fit the application. Follow its WebSocket proxying documentation and test reconnection when an instance is removed. An established connection does not automatically move to another backend.
Track error rate, response time, selected upstream, connection failures, and application saturation. Use a request identifier to connect proxy logs with application logs without recording secrets or unnecessary request payloads.
Run a controlled failure test in a test environment: stop one instance, observe which requests fail, confirm remaining capacity, and then restore the instance. If the proxy reports upstream failures, our Nginx 502 troubleshooting guide can help narrow the cause.
Choose the capability you need next
Start with a reverse proxy when you need a stable public entry point for a private application service. Add load balancing when several suitable application instances need to share requests. Evaluate availability across the whole system and give every extra component a clear operating purpose.
If you are evaluating a hosting control panel, review Core Panel's VPS management capabilities and current documentation against your planned topology. Confirm how the chosen release manages proxy configuration and application services. Core Panel is currently pre-production, so evaluate it on an isolated non-production server before considering a live deployment.
Frequently asked questions
Is Nginx a reverse proxy or a load balancer?
It can perform both roles. Forwarding to one application is a reverse proxy use case; selecting among application instances adds load balancing.
Do I need two separate servers for these roles?
No. One Nginx service can handle both. Separate components may be useful for particular capacity or availability requirements, but the role names do not require separate machines.
Does a load balancer make one VPS highly available?
No. If the proxy and all application instances run on that VPS, a host outage can take them all offline. Host resilience requires a wider design.
Will adding a load balancer make my site faster?
It can help when work can be spread across available application capacity. It will not remove slow queries, external-service delays, or other shared bottlenecks. Measure representative requests before and after the change.